Your Security Awareness & Training Must Address Unintentional Insider Threats
When September rolls around for Insider Threat Awareness Month, many security awareness programs default to the classic narrative: disgruntled employees, corporate espionage, and malicious data theft. But the uncomfortable reality we need to communicate to our workforces is that the vast majority of insider incidents have nothing to do with malice.
Instead, they stem from convenience, exhaustion, and well-meaning shortcuts taken by dedicated employees trying to be productive.
To build a truly strong security culture, your training needs to bridge the gap between how security tools interpret data and how employees actually work. Here is how to refine your messaging to help employees avoid quietly triggering corporate security alarms.
Explain That Security Tools Watch Actions, Not Intent
One of the biggest disconnects for the average employee is understanding how corporate cybersecurity teams monitor the network. Employees know their own intent. They know they’ve been working 60-hour weeks, that their manager asked for a report by 8:00 AM, or that the corporate VPN keeps disconnecting.
But Data Loss Prevention (DLP) tools, User and Entity Behavior Analytics (UEBA), and endpoint detection agents don’t understand intent. They only see behaviors and anomalies:
-
An unencrypted customer database transferred outside the company network.
-
Gigabytes of presentations copied to an unapproved USB drive.
-
An account logged in from two different states within twenty minutes.
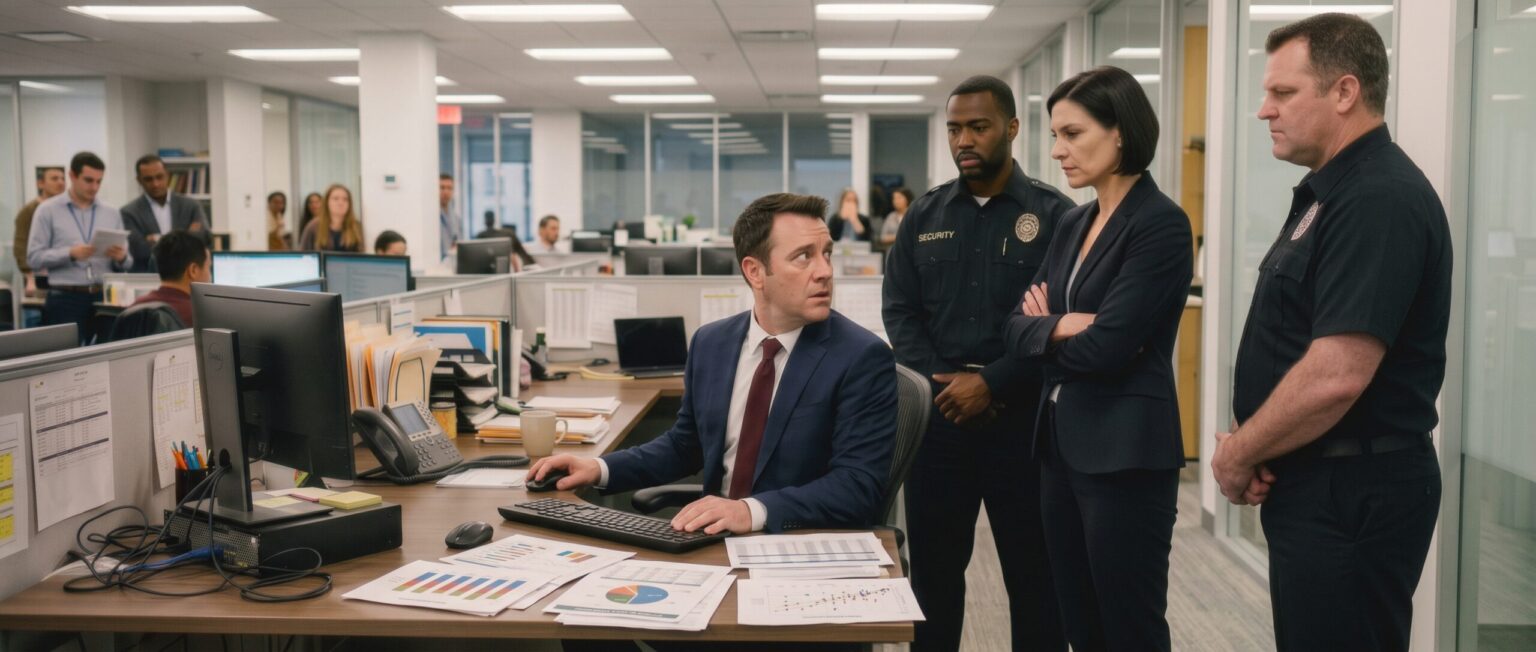
Your awareness content needs to clearly explain that once an alert trips, an investigation begins. Even when an employee is cleared of malicious intent, unauthorized handling of sensitive data can still lead to policy violations, formal HR warnings, or mandated retraining.
5 Everyday Habits to Highlight in Your Next Campaign
To protect your workforce from becoming unintentional insider threats, focus your training efforts on these five common traps.
1. The Personal Email and Cloud “Convenience Shuffle” Employees frequently forward pitch decks, vendor contracts, or spreadsheets to their personal email so they can print them at home or work from the couch.
-
The Training Angle: Explain why DLP systems monitor outbound traffic for sensitive keywords and proprietary markers. Emphasize that personal email accounts rarely have the enterprise-grade protections of corporate systems. Teach the workforce how to use approved enterprise cloud storage for remote work instead of falling back on personal Google Drive or iCloud accounts.
2. Plugging in “Just to Charge” A low phone battery often leads employees to plug their personal devices directly into their work laptop’s USB port.
-
The Training Angle: Most employees don’t realize that modern endpoint protection tools immediately flag any unapproved storage device. To the system, a plugged-in phone looks like potential data exfiltration. Provide clear, practical guidance: always charge personal devices using a dedicated wall brick or an external battery pack.
3. Pasting Sensitive Information into Public AI Tools AI writing assistants have become standard tools for drafting emails or summarizing meeting transcripts. However, pasting internal company information into free, public AI platforms creates severe privacy risks.
-
The Training Angle: Your training must address AI tool usage. Explain that when employees paste confidential customer names, product roadmaps, or proprietary code into a consumer AI tool, that information can be stored on third-party servers and incorporated into future training data. Point them toward your organization’s officially sanctioned, enterprise-protected AI tools.
4. “Hoarding” Files Before a Transition Rumors of corporate restructuring or a planned voluntary job change often prompt employees to gather work samples for their portfolios.
-
The Training Angle: Educate your team on UEBA tools. When an employee suddenly compresses directories into zip files or downloads massive amounts of data, behavior algorithms flag this as high-risk pre-resignation data theft. Remind employees that anything created on company time belongs to the employer, and teach them the official, written process for requesting portfolio materials before they transition roles.
5. Sharing Logins and Bypassing MFA for Speed When a teammate needs emergency access to a dashboard, employees will often share their login or blindly approve an MFA prompt to keep a project moving.
-
The Training Angle: Explain how identity systems track IP addresses and physical locations, which easily triggers “impossible travel” alerts. More importantly, emphasize that account sharing breaks accountability. If a data leak occurs, forensic logs will point solely to the credential owner. Encourage employees to use standard access-request processes, even when they are in a hurry.
Address the “I’m Just Trying to Do My Job!” Mentality
It is completely understandable for employees to feel frustrated when security guardrails slow down an urgent task. In your training materials, acknowledge this friction. Empathize with the fact that enterprise security controls can feel like unnecessary roadblocks.
However, remind them that attackers actively look for these exact same loose seams—unmonitored personal inboxes, unpatched personal devices, and shared credentials.
The ultimate goal of your awareness program should be approachability. Make sure your workforce knows that if an approved process is too clunky, they should talk to the IT or security team. By positioning your security team as partners rather than enforcers, you can help employees find safe, approved alternatives before they resort to risky workarounds.
|
|
For the complete story and tips, read the full article here:https://besecurityaware.com/good-employee-accidentally-becomes-unintentional-insider-threat/ |
No responses yet